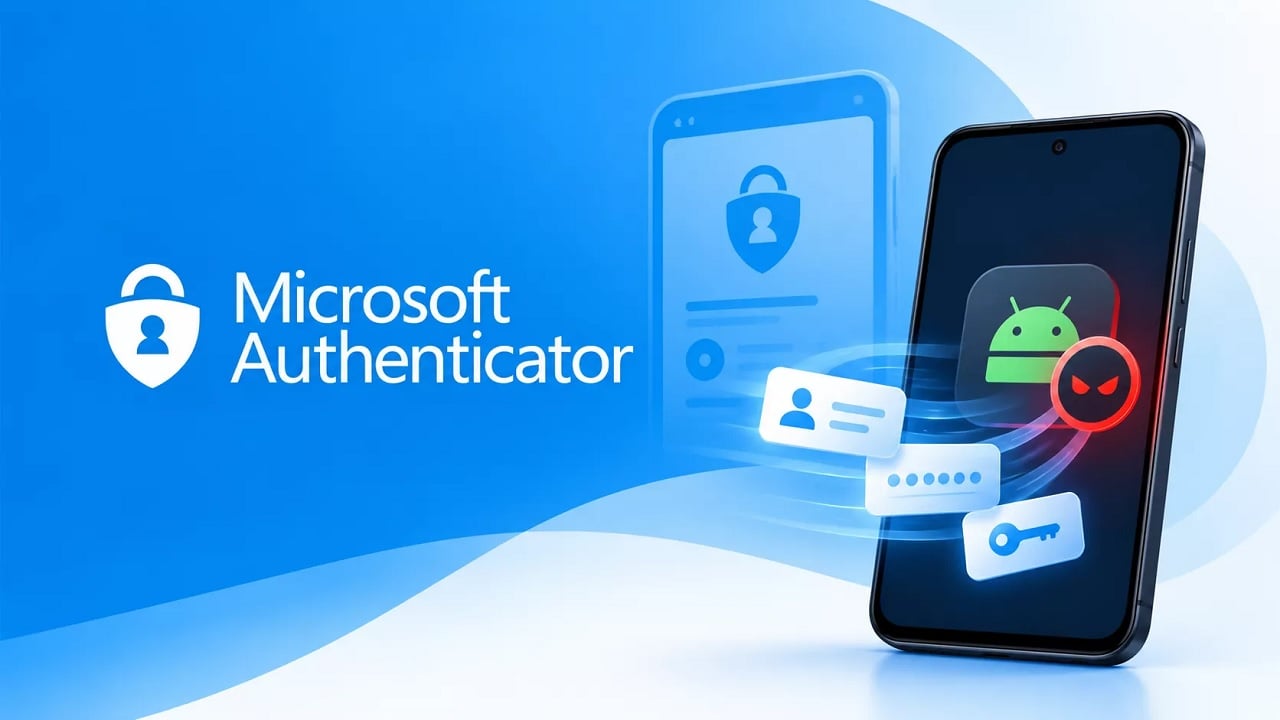
Copyright protected content copied from PhoneWorld website. A security flaw in Microsoft Authenticator for Android could allow malicious apps to steal authentication tokens linked to work accounts without requesting any Android permissions. Microsoft has fixed the vulnerability, which could expose sensitive Microsoft 365 data if attackers successfully exploit it. The vulnerability, tracked as CVE-2026-80097, received a high-severity CVSS score of 8. 6. Microsoft … The post Microsoft Authenticator Flaw Could Let Android Apps Steal Account Tokens Without Permissions appeared first on PhoneWorld.
Microsoft Authenticator Flaw Could Let Android Apps Steal Account Tokens Without Permissions

RELATED ARTICLES